Trust Center
A practical starting point for security and vendor-risk discussions: data, access, hosting, human review, contracts and continuity.
Built for review. Clear about responsibility.
A clear record of the data boundary, the deployment model and the people responsible for the decision.
The data boundary
Your record. Your decision.
Every engagement defines which records the system can access, what it can do with them and where a person must make the decision. Those boundaries belong in the design, the deployment plan and the acceptance tests.
- 01
Client-owned records
Agreed sources, purpose and permissions
- 02
Authorized review
Named approver and recorded decision
- 03
Approved information
Traceable output and agreed access
Client data ownership stays separate from Fourtix platform IP and licensing.
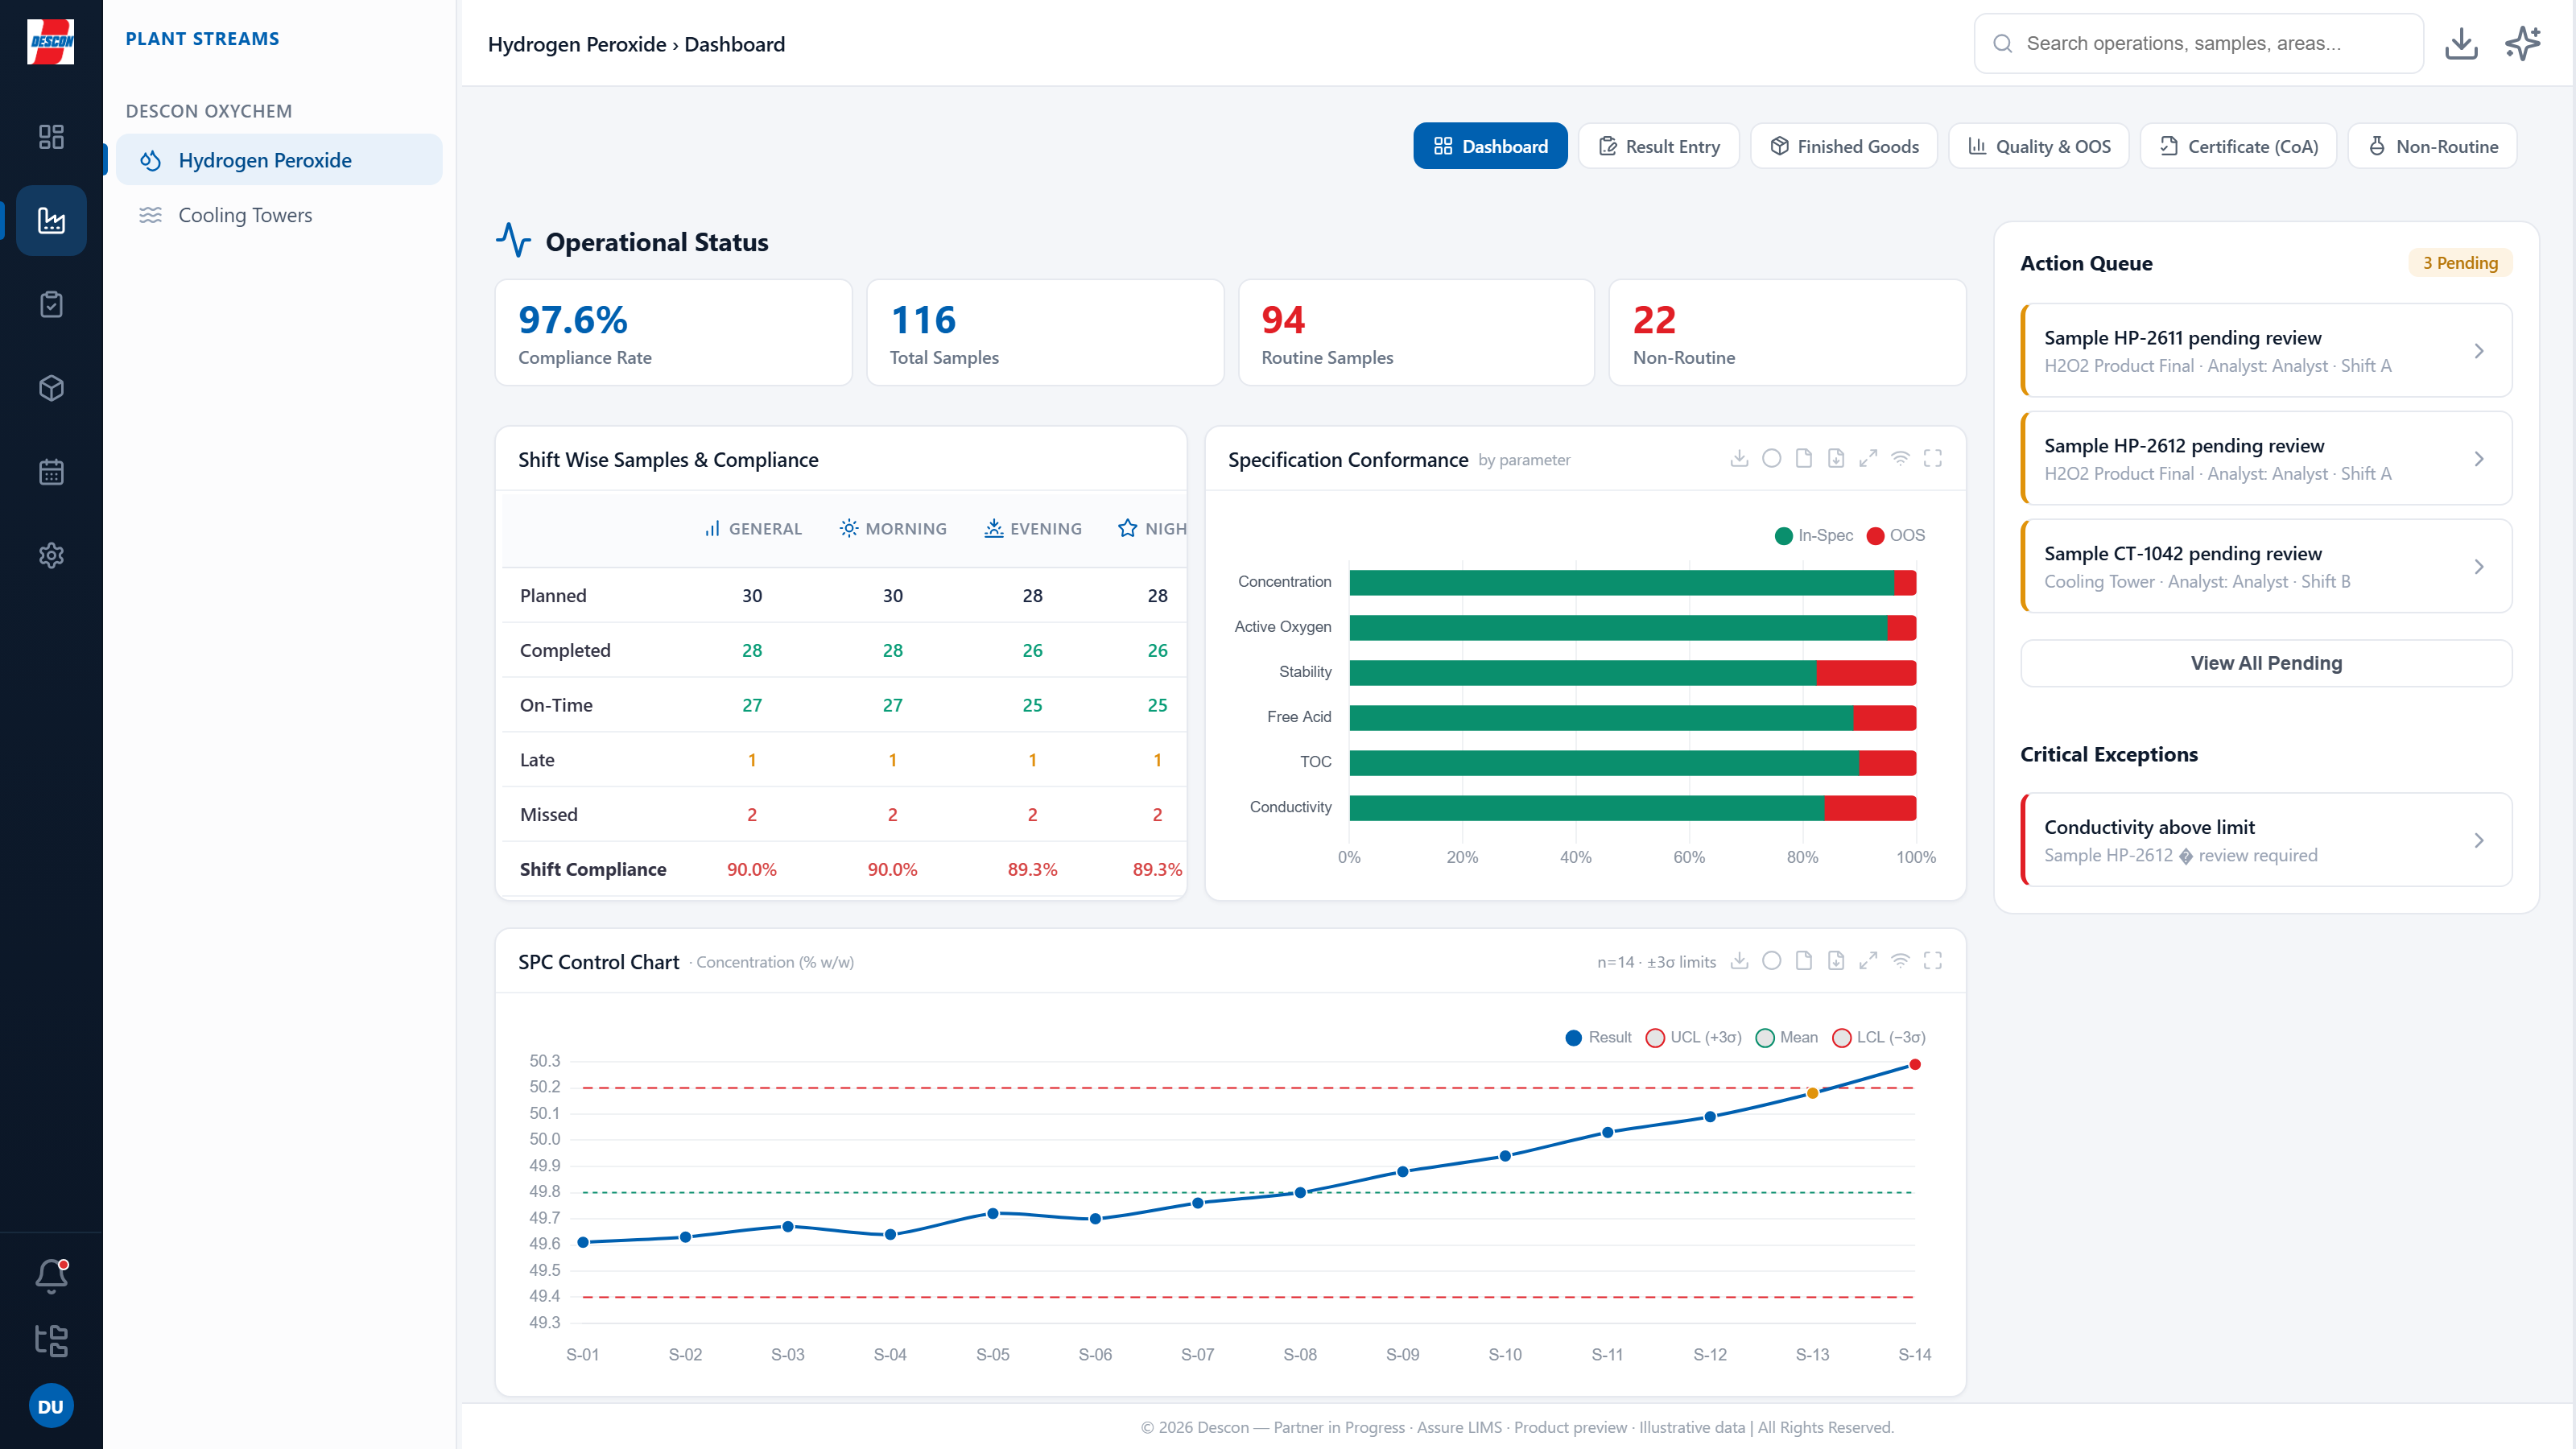
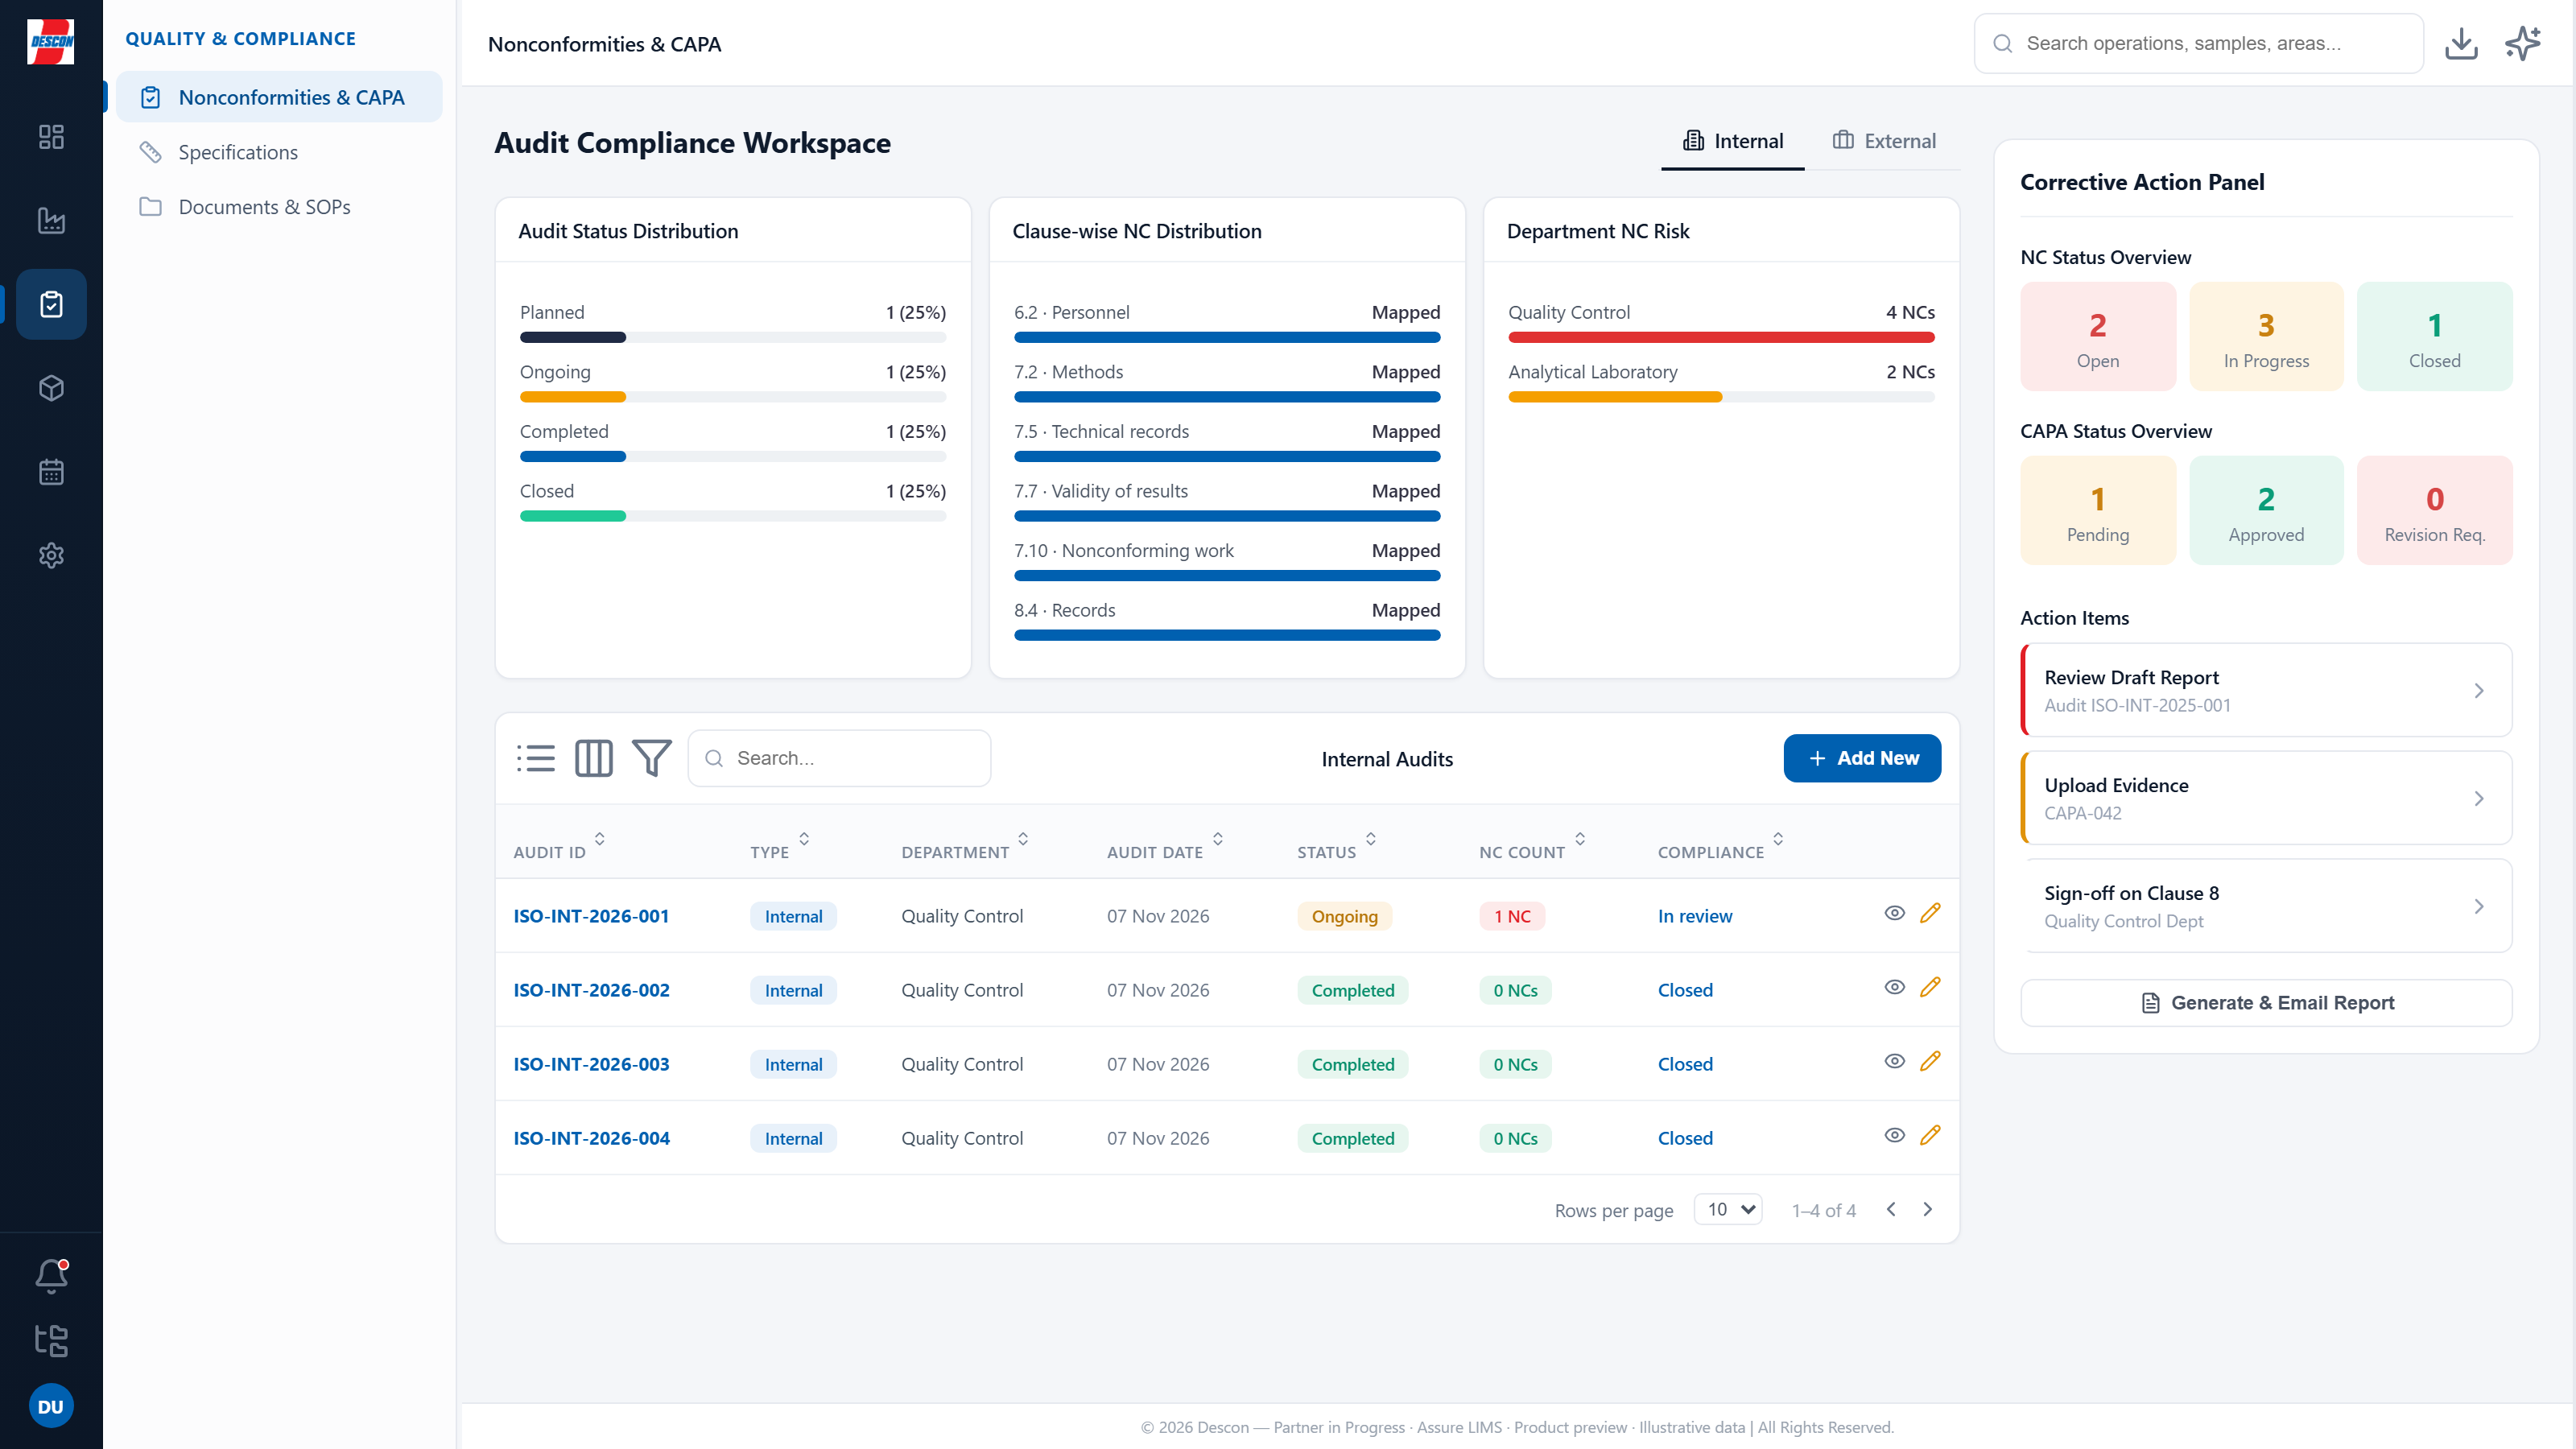
In practice: Assure LIMS
An authorized engineer reviews each laboratory result before it becomes an approved record. The product assistant is read-only.
01Data ownership and handling
- Ownership
Client business, product and operational data remains the client's property. Platform IP and licensing are documented separately.
- Purpose limitation
Use client data only for the agreed engagement. Client records are not used to train models.
- Retention and deletion
Agree retention, export and deletion requirements in the data-processing terms.
- Transport and storage
Define encryption in transit and at rest, backup handling and recovery responsibilities in the deployment plan.
02Access and hosting
- Identity and permissions
Role-based access and Microsoft sign-in where specified. Scope secrets and isolate file storage.
- Deployment options
Fourtix-managed cloud or client infrastructure. Record the hosting region and network boundaries in the statement of work.
- Human approval
No AI-generated regulated action is submitted without a person approving it. The Assure LIMS assistant is read-only.
03Procurement documents
Request the MSA, statement of work, SLA, Data Processing Agreement and acceptance criteria for your engagement. Security questionnaires, subprocessors and implementation-specific controls are reviewed during procurement.
04Incident response
Report a suspected security issue privately to hello@fourtixsystems.com with the affected service, time and a safe description. Please omit sensitive operational data. Named incident contacts, notification windows and escalation responsibilities are agreed in the SLA; no blanket response time is claimed.
05Certifications and roadmap
Fourtix does not claim SOC 2 or ISO/IEC 27001 certification. Readiness work and target dates will be published when formally approved. ISO/IEC 17025 references describe laboratory requirement mapping; software itself is not accredited under that standard.
06Continuity after launch
Documentation, administrator training and knowledge transfer are planned at go-live. Hypercare, maintenance, support coverage and any source-code arrangement are defined in the contract.
The documents behind the engagement.
Request the relevant documents for your review. Signed engagement terms define the actual scope, controls and support commitments.
Master Services Agreement
The responsibilities and commercial framework for the engagement.
Request documentStatement of Work
Scope, deliverables, acceptance criteria and the proposed delivery team.
Request documentData Processing Agreement
Agreed processing purpose, data handling and responsibilities.
Request documentThese links request a copy; they do not imply a public downloadable certification.